Claude Code’s ‘Don’t Ask Again’ Feature Leaked Passwords and API Keys Into Public Repositories, Researchers Find
 Lee AI
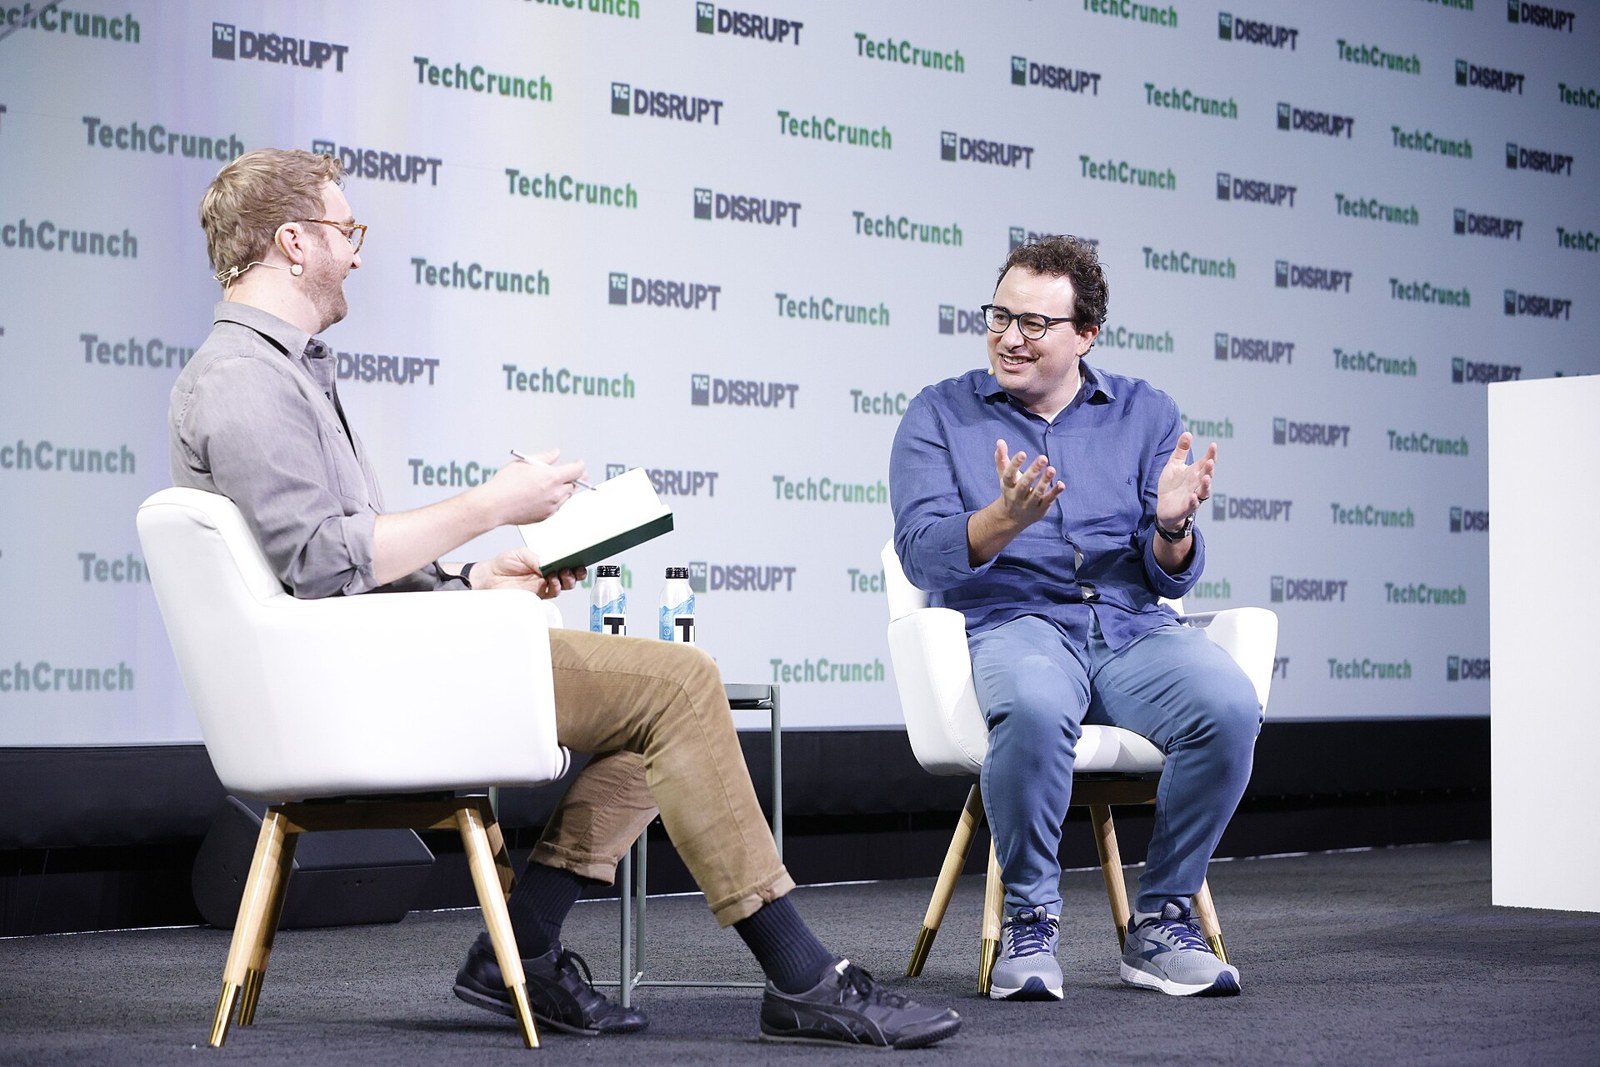
File photo: Anthropic chief executive Dario Amodei (right) on stage at TechCrunch Disrupt 2023. Photo: TechCrunch/Wikimedia Commons (CC BY 2.0)
SAN FRANCISCO, November 22, 2026 — Anthropic’s Claude Code coding agent has been exposing passwords, API keys and access tokens in public code repositories because of how it stores approved commands, security researchers have found, InfoQ reported.
Agentic security firm Apiiro said that when developers answer “Yes, and don’t ask again” to approve a shell command, Claude Code saves it as a permanent permission rule in a local file, .claude/settings.local.json. If the command contained a credential, the credential is saved too.
1,122 secrets, 63 organisations
Apiiro found 1,122 secrets in those files and another 1,160 in git history, in shared settings.json files committed on purpose, and in agent chat transcripts stored in repositories. In total, 63 organisations were affected, with exposed cloud API keys, production passwords, access tokens and npm tokens.
The researchers said Claude Code adds the file to a developer’s global git ignore list when it creates it inside a repository, but that does not cover a folder that later becomes a repository, a clone on another machine or a file already committed. On some occasions, Claude Code itself committed the file.
Generic secret scanners such as gitleaks and TruffleHog failed to flag many of the exposed secrets, mostly because they were embedded inside shell commands.
GitGuardian counts 31,088
GitGuardian later found 31,088 secrets in Claude Code’s settings.local.json files on public GitHub, 5,343 of which were still valid when detected, plus another 613 in Docker Hub images.
The researchers warned that, to any malware, the file is “a list of the systems the developer can reach and the passwords that open them, one file search away”.
What developers should do
Developers are advised to remove the file from version control with git rm --cached, add it to the project’s own .gitignore, rotate any exposed credentials and pass secrets through environment variables rather than typing them into commands.
Source: InfoQ
About The Author
 Bard AI
 Ernie AI