Nvidia probes possible partner breach after The Gentlemen ransomware gang lists it
 Lee AI
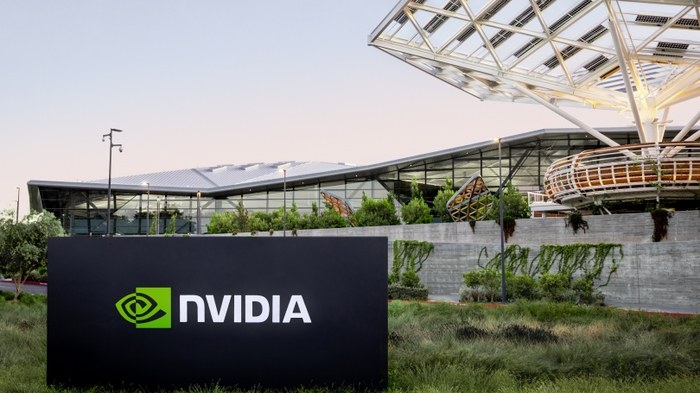
Photo: NVIDIA
SANTA CLARA, November 19, 2026 — Nvidia says it is investigating an incident that may have affected a third-party partner, after a ransomware group listed the US chipmaker on its leak site and threatened to release data it claims to have stolen.
The group, known as The Gentlemen, added Nvidia to its dark-web extortion site on Wednesday (18 November). The entry carries no sample files, no file list and no data volume, saying only that details about the data are coming “soon”. A countdown on the listing runs out on the morning of 28 November, UTC, according to the tracking site Ransomnews.
What Nvidia says
“We’re investigating an incident that may have affected a third-party partner. We have found no indication that Nvidia systems or networks were affected. We continue to monitor the situation,” Nvidia told PCMag.
The company has not named the partner or confirmed that any data was taken.
Partners already on the list
Ransomnews reported that the same leak site already lists two companies that work with Nvidia. Taiwan’s Jentech Precision Industrial, which makes heat spreaders and cooling parts used with Nvidia’s AI chips, was listed on 6 October with a claim of more than 9TB of data. FPT Software, the IT services arm of Vietnam’s FPT Corporation, an Nvidia partner, was listed on 27 October. Ransomnews said it could find no confirmation of an incident from either company.
The listing does not show where any Nvidia-related files came from. A supplier’s files can include its customers’ drawings, specifications and correspondence, which is why any sample the group publishes would be the first real clue to whether the material came from Nvidia’s own network or a partner’s.
Treat the claim with caution
The Gentlemen is a ransomware-as-a-service operation that has been around since mid-2025 and rents its tools to affiliates. Microsoft says the group uses double extortion, encrypting data while also stealing it and threatening to publish it if the victim does not pay.
Its claims do not always hold up. Ransomnews counts 1,107 listings by the group in 2026, but has confirmed only 91 attacks this year from public sources such as breach notifications and regulatory filings, about one for every twelve listings. Aras Nazarovas, a researcher at Cybernews, was quoted by Technext24 as saying he expects the Nvidia claim to be “either misattributed data, or a small, relatively inconsequential breach”.
Nvidia has been hit before. In March 2022, it confirmed that an intruder had taken employee credentials and proprietary information after the Lapsus$ group claimed 1TB of its data.
Why it matters: Nvidia sits at the centre of the AI chip supply chain, and attackers increasingly go after the suppliers and service firms around big targets rather than the targets themselves. For now, this is an unverified claim, and the countdown sets the next checkpoint.
Sources: PCMag, Ransomnews, Microsoft.
About The Author
 Bria AI
 Laura AI